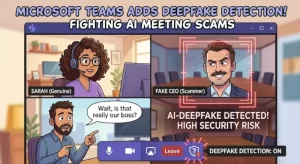
Microsoft Teams is preparing to integrate certified third-party tools that detect synthetic audio and video during meetings, giving organizations new options for identifying potentially manipulated media. The rollout is scheduled to begin in mid-November 2026, with general availability expected by mid-December.
Microsoft is expanding the security capabilities available to Teams customers as AI-generated voices, faces, and video become increasingly relevant to workplace identity verification. The planned feature will allow certified third-party detection providers to analyze meeting media and send signals to Teams, where supported experiences and controls can help participants make more informed trust decisions.
The update is listed under Microsoft 365 Roadmap ID 573451 and remains in development. Rather than performing the detection itself, Microsoft Teams will provide the integration layer that connects participating detection services with the meeting experience.
For IT administrators, the announcement introduces an important planning consideration: organizations will need to select a supported provider, deploy its application, grant the necessary permissions, and configure the appropriate meeting policies before using the capability.
Microsoft Teams Deepfake Detection: What’s Changing?
The upcoming feature will enable organizations to integrate certified third-party synthetic audio and video detection solutions into Microsoft Teams meetings.
These providers will examine meeting media for indications that audio or video may have been generated or manipulated artificially. They will then send detection signals to Teams, enabling the platform to surface information and support relevant in-meeting controls.
The distinction between detection and integration is important. Microsoft has explicitly stated that the third-party provider performs the synthetic media analysis, while Teams supplies the platform integration and experiences used to surface and act on detection signals.
The planned capability is intended to help organizations identify potential deepfake threats without requiring every business to build its own detection technology.
Key details include:
- Product: Microsoft Teams.
- Feature: Third-party synthetic audio and video detection.
- Provider requirement: Certified third-party detection solutions.
- Roadmap reference: Microsoft 365 Roadmap ID 573451.
- Targeted Release: Mid-November to late November 2026.
- General Availability: Late November to mid-December 2026.
These dates represent Microsoft’s announced rollout targets, not a guarantee that every organization will receive the feature on the same day.
Why Deepfake Detection Matters for Workplace Meetings
Video meetings have become a routine part of business operations, supporting everything from internal planning and customer relationships to financial approvals and executive decision-making.
That convenience also creates opportunities for impersonation. A convincing synthetic voice or manipulated video can make a person appear to be someone they are not, potentially influencing colleagues who rely on familiar voices, faces, and meeting contexts to establish trust.
In a business environment, the consequences could extend beyond an uncomfortable meeting. An impersonation attempt might be used to support fraudulent payment requests, obtain confidential information, manipulate employees into disclosing credentials, or exploit trust between colleagues and business partners.
Traditional security controls remain essential, but they do not always answer a particular question: does the audio or video presented during a live meeting appear to be authentic?
Third-party synthetic media detection aims to help address that challenge by adding another source of information to the meeting environment.
The capability should be viewed as an additional security layer rather than a complete solution to identity fraud. A suspicious-media signal can inform a decision, but organizations will still need processes for verifying identities and handling sensitive requests.
How Third-Party Synthetic Media Detection Will Work
The planned integration establishes a relationship between the detection provider and the Teams meeting experience.
The process can be understood in three stages.
1. A supported provider analyzes meeting media
An organization selects and deploys a certified detection solution. The provider analyzes relevant audio or video signals for indicators of synthetic or manipulated media, subject to its capabilities and data-processing arrangements.
2. The provider sends a detection signal to Teams
When the provider identifies media it considers potentially synthetic, it can communicate a detection signal through the supported integration. The signal originates from the provider’s analysis, rather than from an independent deepfake-detection engine operated by Teams as part of this feature.
3. Teams surfaces the signal through supported experiences
Teams provides the integration and in-meeting experiences for presenting and acting on detection information. This is intended to help organizations and meeting participants make more informed trust decisions.
Microsoft’s announcement does not establish that every form of deepfake will be detected, nor does it promise perfect accuracy. Detection performance will depend on the selected provider, its technology, and the circumstances in which it analyzes media.
Organizations should therefore evaluate what a provider detects, how it communicates uncertainty, and how users are expected to respond when a signal appears.
Rollout Schedule: When Will the Feature Arrive?
Microsoft has outlined a phased worldwide rollout for the new capability.
| Release phase | Planned timeline |
|---|---|
| Targeted Release | Begins mid-November 2026; expected to finish by late November |
| General Availability | Begins late November 2026; expected to finish by mid-December |
The phased approach gives organizations an opportunity to prepare before the feature becomes generally available.
As of October 16, 2026, the feature is still in development. Administrators should monitor the Microsoft 365 roadmap and their organization’s Microsoft 365 Message Center for updates, including any changes to deployment dates or implementation requirements.
The schedule should be treated as a planning estimate. Availability may not be simultaneous across all tenants.
What IT Administrators Need to Do Before Deployment
The new capability will require administrative preparation. Organizations should not assume that deepfake detection will automatically activate for every Teams meeting when the rollout begins.
Microsoft’s guidance identifies several actions administrators should take.
1. Evaluate and select a supported provider
Start by assessing certified third-party detection solutions that can integrate with Teams.
Consider detection coverage, expected accuracy, deployment requirements, support arrangements, pricing, and compatibility with the organization’s existing security architecture. The provider’s ability to explain its findings and limitations should also factor into the decision.
2. Review privacy and compliance requirements
Because the provider may analyze meeting audio and video signals, organizations should understand exactly what data is processed and how that information is handled.
Review the provider’s terms, privacy documentation, retention practices, security controls, and compliance commitments. Determine whether the proposed processing is compatible with internal policies and any applicable contractual or regulatory obligations.
3. Deploy the provider application
Administrators should deploy the selected provider’s app through Manage apps in the Teams admin center, following the provider’s documented setup requirements.
The organization should also verify any prerequisites for enabling the integration and confirm that the application comes from the supported provider it has evaluated.
4. Grant the required permissions
The integration may require permissions that allow the provider to participate in the supported meeting workflow and report detection information.
Grant only the permissions required for the intended deployment. Security teams should understand the scope of those permissions, the data accessible to the app, and the consequences of authorizing them.
5. Configure the relevant Teams meeting policies
Administrators should review and configure applicable meeting policies so the feature operates in accordance with the organization’s requirements.
Before wider deployment, test the experience with a limited group of users. Confirm that detection information is presented as expected and that employees understand the appropriate response to a warning or suspicious signal.
Security and Compliance: Questions Organizations Should Ask
Integrating third-party detection into a collaboration platform can improve visibility, but it also introduces governance responsibilities.
The most immediate consideration is data handling. Audio and video from business meetings may contain personal information, confidential commercial discussions, customer details, or sensitive internal material.
Before enabling a provider, security, privacy, and compliance teams should establish clear answers to the following questions:
- What meeting data does the provider process, and for what purpose?
- Is the analysis performed in real time, and what information is retained afterward?
- Where is the data processed and stored?
- Does the provider share data with other service providers?
- How are access, deletion, retention, and incident response managed?
- What permissions does the app require, and who approves them?
- How will users be informed about detection signals and their limitations?
These questions are particularly important for organizations operating across multiple jurisdictions or handling regulated information.
Administrators should also establish how detection signals fit into existing incident-response procedures. For example, a suspected impersonation attempt involving a payment instruction should trigger independent verification through an established channel rather than relying solely on a media-detection result.
What the Feature Can—and Cannot—Guarantee
The integration gives organizations a way to bring third-party synthetic media detection into their Teams environment. Its practical value, however, will depend on how effectively the technology is implemented and used.
Potential benefits include:
- Additional meeting security: Detection signals can provide another source of information when assessing suspicious audio or video.
- Greater deployment flexibility: Organizations can select a supported provider that aligns with their operational and compliance requirements.
- More informed decisions: Integrated detection information may help users question suspicious media before acting on a request.
- Centralized administration: IT teams can manage application deployment, permissions, and relevant meeting policies through established administrative processes.
There are also important limitations to consider.
A detection signal is not definitive proof of fraud, just as the absence of a signal is not proof that a participant is genuine. Detection tools can have false positives and false negatives, and their performance may vary with the media quality, type of manipulation, and techniques used by attackers.
Organizations should avoid treating an automated result as the sole basis for high-impact decisions. Human verification, strong authentication, access controls, and established approval processes remain necessary.
The Bigger Picture: AI Security Is Becoming a Meeting-Room Issue
Microsoft’s planned integration reflects a broader security challenge for organizations adopting AI-enabled communication tools: businesses must consider not only who has access to a meeting, but also whether the media presented by a participant can be trusted.
This distinction matters because familiar communication habits are often built on assumptions about identity. Employees may recognize a manager’s voice or face and feel comfortable responding quickly to an urgent request. Synthetic media can undermine that confidence, particularly when combined with social engineering.
The most effective response is unlikely to come from a single detection feature. Organizations will need multiple layers of protection, combining technical detection with identity verification, employee awareness, and clear procedures for sensitive transactions.
For example, a company could instruct employees to confirm unusual payment requests using a separate, previously established communication channel, regardless of whether the request arrives through a familiar-looking Teams meeting.
The new integration could support that approach by giving employees another warning signal to consider, while existing security controls provide the broader safeguards.
What Happens Next?
The immediate priority for Microsoft Teams customers is preparation rather than assuming the feature is already available.
Organizations should identify their likely use cases, evaluate certified providers, review data-processing implications, and plan the administrative work required to deploy the integration. IT teams should also prepare user guidance explaining what detection signals mean and why they should not replace independent verification.
With Targeted Release scheduled to begin in mid-November 2026 and General Availability expected to extend into mid-December, the coming weeks will provide a clearer picture of how the feature reaches customers and how supported providers implement it.
The longer-term question is how well detection integrates into everyday security decisions. If organizations can combine useful signals with sensible policies and employee training, Microsoft Teams’ third-party detection capability could become a practical addition to defenses against AI-enabled impersonation.
Extra posts:
 Microsoft Teams Rooms Gets Smarter: AI-Powered Facilitator Brings Real-Time Meeting Notes to Physical Meeting Rooms
 Microsoft Teams Gets Smarter With Personalized Multilingual Meeting Recaps
 Microsoft Teams Is Getting a Smarter Meeting Assistant: Facilitator Can Now Join Channel Meetings
 Microsoft Teams Adds In-Meeting AI Toggle: Users Gain More Control Over Copilot and Facilitator
 Microsoft Teams Introduces AI Meeting Recap Without Transcripts, Helping Organizations Balance Productivity and Compliance
 Microsoft Teams to Blur QR Codes From External Users by Default in New Security Update