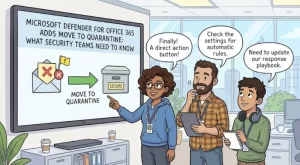
Microsoft is introducing a new Move to Quarantine remediation action in Microsoft Defender for Office 365 Plan 2, giving security administrators another way to contain suspicious emails that have already reached users’ mailboxes. The feature is scheduled for worldwide general availability beginning in early November 2026, with rollout expected to finish by mid-December 2026.
The new action will allow authorized administrators to move selected email messages directly into Microsoft Defender quarantine from supported mailbox locations. This gives security teams greater control over suspicious messages while preserving options to investigate, release, or permanently delete them according to the applicable quarantine policy.
For organizations using Microsoft Defender for Office 365 Plan 2, the update introduces an additional remediation option across several security investigation and response experiences, including Threat Explorer, Advanced Hunting, custom detection rules for email results, email entity and summary experiences, and the Unified Action Center.
What Is the New Move to Quarantine Feature?
The new Move to Quarantine action is designed to help security teams contain potentially malicious emails without relying solely on deletion or moving messages to users’ Junk Email folders.
Email threats do not always get caught before delivery. A suspicious message may initially pass security checks and reach an employee’s inbox before subsequent investigation reveals a threat. In these situations, administrators need a way to remove the message from the user’s accessible mailbox while retaining control over what happens next.
Move to Quarantine addresses this operational need by transferring selected messages from supported mailbox locations into Microsoft Defender quarantine.
Once a message is quarantined, authorized users can investigate it and take further action based on the organization’s security policies. Depending on the permissions and quarantine policy in effect, they may be able to preview the message, release it, or permanently delete it.
The change is intended to make email threat containment more flexible without replacing the remediation actions administrators already use.
When Will Microsoft Roll Out the Update?
Microsoft’s announcement outlines the following deployment window:
- Rollout start: Early November 2026.
- Expected completion: Mid-December 2026.
- Availability: Worldwide general availability.
- Eligible service: Microsoft Defender for Office 365 Plan 2, including eligible Microsoft 365 subscriptions that contain Plan 2.
The deployment will introduce the new action to authorized administrators as it becomes available in the relevant security experiences.
Organizations do not need to enable the feature manually. However, administrators should review their quarantine policies and operational procedures before the rollout reaches their environments.
Because the rollout is scheduled to take place over several weeks, security teams should also account for the possibility that the option may not appear in every environment at the same time.
Where Will Administrators Find the New Action?
Move to Quarantine will be available through several Microsoft Defender for Office 365 investigation and remediation experiences.
These include:
- Threat Explorer: Supports investigations into suspicious email activity and helps security teams select messages for remediation.
- Advanced Hunting: Allows analysts to investigate email-related security data and review relevant action details.
- Custom detection rules for email results: Extends the available remediation choices in supported email detection workflows.
- Email entity and email summary experiences: Provides access to message-related investigation and response actions.
- Unified Action Center: Tracks remediation actions and their statuses, helping administrators review the progress and outcome of response activities.
The availability of the action across these experiences is relevant to security operations teams that investigate incidents through different workflows. Analysts can use the appropriate supported interface rather than treating quarantine as a separate, disconnected process.
Microsoft also states that the remediation action and its status will be tracked in the Unified Action Center and related investigation experiences. This provides a record of the administrative response and helps teams understand whether remediation was completed.
How Move to Quarantine Works
When an authorized administrator selects Move to Quarantine, the selected email messages are removed from supported user-accessible mailbox locations and placed in Microsoft Defender quarantine.
The supported source locations include:
- Inbox
- Junk Email
- Deleted Items
- Recoverable soft-deleted locations
Messages in unsupported locations are not brought into scope by this update. These include hard-deleted messages and messages stored in on-premises or external mailboxes.
Administrators can also select a quarantine policy when using the action. That policy determines how end users may interact with the quarantined messages. By default, access to quarantined messages is restricted to administrators.
This distinction matters because quarantine is not simply another mailbox folder. It provides a controlled environment in which access and subsequent actions depend on the applicable permissions and policy settings.
Quarantined messages will be identified with the reason Admin triggered, distinguishing them from messages quarantined for other reasons.
If a message is later approved for release, releasing it from quarantine delivers it to the user’s Inbox. Authorized users can also preview or permanently delete quarantined messages where permitted by the applicable policy and their assigned permissions.
The action therefore gives security teams an intermediate containment option: remove a suspicious email from the user’s mailbox while retaining the ability to investigate it before deciding on its final disposition.
What Happens If Some Messages Cannot Be Moved?
Email remediation operations do not always succeed for every selected message. Microsoft states that eligible messages will continue processing when one or more messages cannot be moved.
Administrators can review the results to identify partial failures and determine which messages still require attention.
This behavior is important in investigations involving multiple emails, where stopping an entire operation because of an individual failure could delay containment of other eligible messages.
Security teams should incorporate result checking into their response procedures rather than assuming that submitting a remediation action guarantees that every selected message has been successfully quarantined.
The Unified Action Center and related investigation experiences will help administrators review action statuses and follow up on incomplete operations.
Required Permissions and Administrative Controls
The new remediation action is intended for authorized security administrators, and the existing permission model remains relevant.
According to Microsoft’s announcement, the Search and Purge role is required to approve remediation actions. Organizations should verify that the appropriate administrators have the necessary role assignments before incorporating Move to Quarantine into their incident response workflows.
Administrators should also understand how quarantine policies affect message visibility and release permissions. A successful move into quarantine does not automatically mean that every end user can access or release the message.
Before the rollout, security teams should review the following controls:
- Confirm which administrators are authorized to approve remediation actions.
- Verify that the required Search and Purge role is assigned appropriately.
- Review quarantine policies and determine who can preview, release, or permanently delete messages.
- Ensure incident response documentation explains how to validate remediation results.
- Train analysts to distinguish administrator-triggered quarantine from other quarantine reasons.
These steps can help organizations introduce the feature without creating confusion about access rights, approval requirements, or the status of an investigated email.
What Existing Microsoft Defender Capabilities Will Remain Unchanged?
Microsoft has clarified that the new action does not replace existing remediation functionality.
The following actions will remain available:
- Move to Junk
- Move to Deleted Items
- Soft delete
- Hard delete
The announcement also states that the update will not change threat verdict assignments, existing remediation approval workflows and permissions, Automated Investigation and Response (AIR) actions, or Microsoft Graph API capabilities.
Messages in unsupported locations will remain outside the scope of the new action, including hard-deleted messages and those held in on-premises or external mailboxes.
For security operations teams, this means Move to Quarantine should be treated as an additional response option rather than a wholesale change to existing email security workflows.
The appropriate action will continue to depend on the investigation findings, organizational policy, available permissions, and the desired outcome for each message.
Why This Update Matters for Email Security Teams
The main operational benefit is the ability to separate containment from final disposition.
Moving a suspicious message to quarantine removes it from the user’s accessible mailbox locations while allowing authorized personnel to investigate it further. This can be useful when an organization needs to prevent additional interaction with a message but has not yet decided whether it should be released or permanently deleted.
The policy-based approach also gives organizations control over who can access quarantined messages and what actions they may take. That flexibility can help security teams align remediation with their internal incident response and access-control requirements.
There are practical considerations, however. Administrators need to understand the differences between quarantine, deletion, and moving a message to Junk Email. They must also verify action results and account for messages that cannot be moved because they are in unsupported locations or otherwise fail remediation.
The new feature does not eliminate the need for detection, investigation, permissions management, or follow-up. Instead, it adds another option to the response process after a potentially malicious message has been identified.
Recommended Actions Before the November 2026 Rollout
Microsoft says no action is required to enable the capability, but recommends that organizations prepare their security operations teams.
IT and security administrators should prioritize four areas:
Review quarantine policies. Confirm whether the default administrator-only access model meets the organization’s needs and determine which users or administrators should be permitted to interact with quarantined messages.
Verify administrator permissions. Ensure that the appropriate personnel have the Search and Purge role required to approve remediation actions.
Update incident response playbooks. Document when Move to Quarantine should be used instead of moving a message to Junk Email, deleting it, or taking another remediation action.
Update training and operational documentation. Inform security analysts and incident responders about the new option, the Admin triggered quarantine reason, and the importance of checking remediation results for partial failures.
Organizations can also consult Microsoft’s documentation on remediating malicious email delivered in Office 365. The supplied announcement notes that this documentation is expected to be updated during the rollout.
What Organizations Should Watch Next
As the worldwide rollout progresses from November into December 2026, administrators should monitor the availability of Move to Quarantine in their Defender environments and confirm that the associated investigation and remediation workflows behave as expected.
The key questions will be whether the relevant administrators can access the action, whether quarantine policies reflect the organization’s intended access controls, and whether incident response teams can reliably verify the outcome of remediation operations.
The introduction of Move to Quarantine gives Microsoft Defender for Office 365 Plan 2 customers another way to manage suspicious email after delivery. Its practical value will depend on how well organizations integrate the action into their existing permissions, investigation procedures, and quarantine policies.
For security teams preparing for the update, reviewing those controls now will help ensure that the new option can be used consistently when it becomes available.
Extra posts:
 Microsoft Defender for 365 Your All-in-One Security Shield for Modern Threats
 Microsoft Defender for Office 365 Is Changing How Promotional Emails Are Handled
 Microsoft Teams Adds Mandatory Participant Consent Before Meetings: What Admins Need to Know
 Microsoft Teams Adds In-Meeting AI Toggle: Users Gain More Control Over Copilot and Facilitator
 Microsoft 365 Security Made Simple What Non-IT Teams Must Know
 Microsoft 365 Adds New Copilot Governance Control for Advanced Agents and Plugins